

[Nov 11, 2022] CS0-002 Exam Dumps, CS0-002 Practice Test Questions
Free CS0-002 Study Guides Exam Questions and Answer
Software & Systems Security: 18%
- Applying security solutions to infrastructure management: the candidates will demonstrate their understanding of Cloud vs. on-premise, assess management, segmentation, network architecture, change management, virtualization, containerization, identity & access management, encryption, active defense, monitoring, and logging.
- Explaining software assurance best practices: this topic requires the learners’ understanding of platforms, DevSecOps, secure coding best practices, software development life cycle integration, and dynamic analysis tools.
- Explaining hardware assurance best practices: this will measure the knowledge of eFuse, unified extensible firmware interface, trusted foundry, secure processing, self-encrypting drive, bus encryption, measured boot and attestation, and trusted firmware updates.
How can you prepare for CompTIA CS0-002 exam?
The candidates can find a wealth of resources to prepare for the CS0-002 exam on the official website. They can purchase the CompTIA Training Bundle directly from the certification webpage. The content of the bundle includes:
- Official CySA+ Self-Paced Study Guide (eBook)
- Exam Retake
- Exam Voucher
- CompTIA CertMaster Practice for Cybersecurity Analyst
- CompTIA CertMaster Learn for Cybersecurity Analyst
CompTIA also offers alternative training options, which include virtual labs, instructor-led training, and video tutorials. The details and links to these learning resources can be found on the official website. Before commencing the preparation process, it is recommended that the applicants first go through the study guide to be able to understand the comprehensive knowledge areas that will be evaluated during the delivery of the exam.
NEW QUESTION 146
During a quarterly review of user accounts and activity, a security analyst noticed that after a password reset the head of human resources has been logging in from multiple locations, including several overseas. Further review of the account showed access rights to a number of corporate applications, including a sensitive accounting application used for employee bonuses.
Which of the following security methods could be used to mitigate this risk?
- A. Privilege escalation restrictions
- B. Elimination of self-service password resets
- C. RADIUS identity management
- D. Context-based authentication
Answer: D
NEW QUESTION 147
While reviewing a cyber-risk assessment, an analyst notes there are concerns related to FPGA usage. Which of the following statements would BEST convince the analyst's supervisor to use additional controls?
- A. FPGAs are expensive and can only be programmed once. Code deployment safeguards are needed.
- B. FPGAs are expensive to produce. Anti-counterierting safeguards are needed.
- C. FPGAs have an inflexible architecture. Additional training for developers is needed
- D. FPGAs are vulnerable to malware installation and require additional protections for their codebase.
Answer: B
Explanation:
Ethernet switches are mass-produced and offered at discounts on not so widely-used chips with massive economies of scale. While in case of FPGAs,they are used as Ethernet switches and hence cost more since the expense of development and infrastructure are distributed among fewer clients.
NEW QUESTION 148
A custom script monitors real-time
- A. SAML logging is not supported for cloud-based authentication.
- B. Log data may be visible to other customers.
- C. Logs may contain incorrect information
- D. Access to logs may be delayed for some time.
Answer: D
NEW QUESTION 149
While conoXicting a cloud assessment, a security analyst performs a Prowler scan, which generates the following within the report: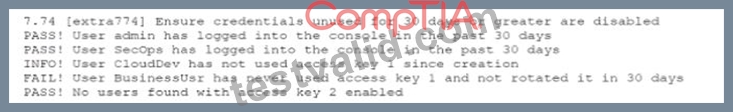
Based on the Prowler report, which of the following is the BEST recommendation?
- A. Delete BusinessUsr access key 1.
- B. Delete access key 2.
- C. Delete access key 1.
- D. Delete Cloud Dev access key 1
Answer: B
NEW QUESTION 150
Due to new regulations, a company has decided to institute an organizational vulnerability management program and assign the function to the security team.
Which of the following frameworks would BEST support the program? (Select two.)
- A. ITIL
- B. ISO 27000 series
- C. NIST
- D. COBIT
- E. OWASP
Answer: A,C
NEW QUESTION 151
A threat intelligence analyst who works for a financial services firm received this report:
"There has been an effective waterhole campaign residing at
www.bankfinancecompsoftware.com. This domain is delivering ransomware. This ransomware variant has been called "LockMaster" by researchers due to its ability to overwrite the MBR, but this term is not a malware signature. Please execute a defensive operation regarding this attack vector." The analyst ran a query and has assessed that this traffic has been seen on the network.
Which of the following actions should the analyst do NEXT? (Select TWO).
- A. Format the MBR as a precaution
- B. Advise the security architects to enable full-disk encryption to protect the MBR
- C. Visit the domain and begin a threat assessment
- D. Advise the security analysts to add an alert in the SIEM on the string "LockMaster"
- E. Produce a threat intelligence message to be disseminated to the company
- F. Advise the firewall engineer to implement a block on the domain
Answer: B,C
NEW QUESTION 152
During routine monitoring, a security analyst discovers several suspicious websites that are communicating with a local host. The analyst queries for IP 192.168.50.2 for a 24-hour period: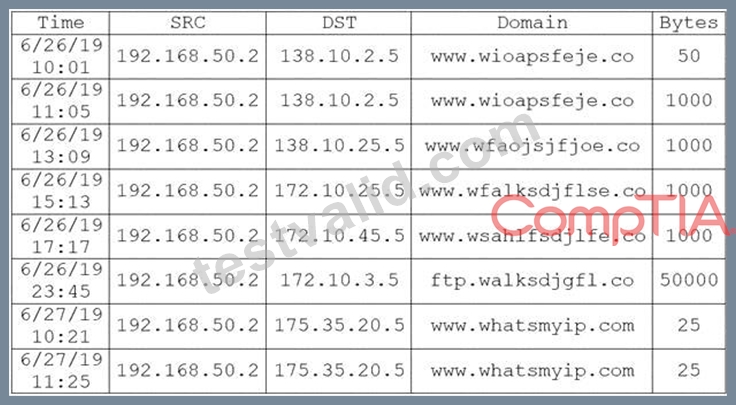
To further investigate, the analyst should request PCAP for SRC 192.168.50.2 and.
- A. DST 138.10.25.5.
- B. DST 138.10.2.5.
- C. DST 172.10.45.5.
- D. DST 175.35.20.5.
- E. DST 172.10.3.5.
Answer: E
NEW QUESTION 153
A security analyst on the threat-hunting team has developed a list of unneeded, benign services that are currently running as part of the standard OS deployment for workstations. The analyst will provide this list to the operations team to create a policy that will automatically disable the services for all workstations in the organization.
Which of the following BEST describes the security analyst's goal?
- A. To optimize system performance
- B. To create a system baseline
- C. To improve malware detection
- D. To reduce the attack surface
Answer: D
NEW QUESTION 154
An organization recently discovered that spreadsheet files containing sensitive financial data were improperly stored on a web server. The management team wants to find out if any of these files were downloaded by pubic users accessing the server. The results should be written to a text file and should induce the date. time, and IP address associated with any spreadsheet downloads. The web server's log file Is named webserver log, and the report We name should be accessreport.txt. Following is a sample of the web servefs.log file:
2017-0-12 21:01:12 GET /index.htlm - @4..102.33.7 - return=200 1622
Which of the following commands should be run if an analyst only wants to include entries in which spreadsheet was successfully downloaded?
- A. more webserver.log | grep -A *.xIs < accessreport.txt
- B. more webserver.log | grep * xIs > accessreport.txt
- C. more webserver.log | grep ' -E ''return=200 | accessreport.txt
- D. more webserver.log > grep ''xIs > egrep -E 'success' > accessreport.txt
Answer: C
NEW QUESTION 155
A company's marketing emails are either being found in a spam folder or not being delivered at all. The security analyst investigates the issue and discovers the emails in question are being sent on behalf of the company by a third party in1marketingpartners.com Below is the exiting SPP word:
Which of the following updates to the SPF record will work BEST to prevent the emails from being marked as spam or blocked?
A)
B)
C)
D)
- A. Option B
- B. Option D
- C. Option A
- D. Option C
Answer: A
NEW QUESTION 156
A security analyst is reviewing the logs from an internal chat server. The chat.logfile is too large to review manually, so the analyst wants to create a shorter log file that only includes lines associated with a user demonstrating anomalous activity. Below is a snippet of the log: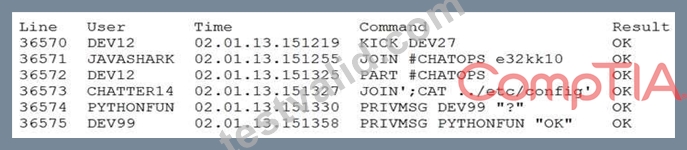
Which of the following commands would work BEST to achieve the desired result?
- A. grep -v pythonfun chat.log
- B. grep -i chatter14 chat.log
- C. grep -v chatter14 chat.log
- D. grep -i pythonfun chat.log
- E. grep -i javashark chat.log
- F. grep -v javashark chat.log
Answer: F
NEW QUESTION 157
Given the following log snippet: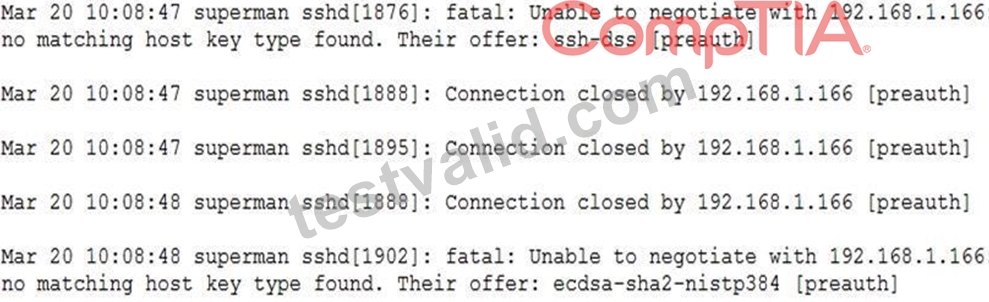
Which of the following describes the events that have occurred?
- A. An attempt to make an SSH connection from outside the network was done using PKI.
- B. An attempt to make an SSH connection from an unknown IP address was done using a password.
- C. An attempt to make an SSH connection from 192.168.1.166 was done using PKI.
- D. An attempt to make an SSH connection from "superman" was done using a password.
Answer: C
NEW QUESTION 158
A security analyst is investigating a compromised Linux server. The analyst issues the ps command and receives the following output.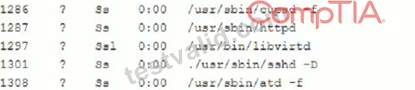
Which of the following commands should the administrator run NEXT to further analyze the compromised system?
- A. /bin/la -1 /proc/1301/exe
- B. kill -9 1301
- C. strace /proc/1301
- D. rpm -V openash-server
Answer: C
NEW QUESTION 159
Which of the following describes why it is important for an organization's incident response team and legal department to meet and discuss communication processes during the incident response process?
- A. To predetermine what details should or should not be shared with internal or external parties in the event of an incident
- B. To comply with existing organization policies and procedures on interacting with internal and external parties
- C. To identify which group will communicate details to law enforcement in the event of a security incident
- D. To ensure all parties know their roles and effective lines of communication are established
Answer: B
NEW QUESTION 160
External users are reporting that a web application is slow and frequently times out when attempting to submit information.
Which of the following software development best practices would have helped prevent this issue?
- A. Regression testing
- B. Input validation
- C. Stress testing
- D. Fuzzing
Answer: C
NEW QUESTION 161
A security analyst has received reports of very slow, intermittent access to a public-facing corporate server.
Suspecting the system may be compromised, the analyst runs the following commands: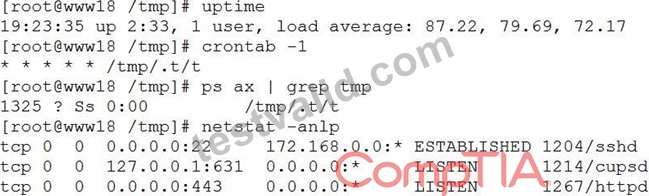
Based on the output from the above commands, which of the following should the analyst do NEXT to further the investigation?
- A. Perform a binary analysis on the /tmp/.t/t file, as it is likely to be a rogue SSHD server.
- B. Run crontab -r; rm -rf /tmp/.t to remove and disable the malware on the system.
- C. Run kill -9 1325 to bring the load average down so the server is usable again.
- D. Examine the server logs for further indicators of compromise of a web application.
Answer: D
NEW QUESTION 162
For machine learning to be applied effectively toward security analysis automation, it requires
__________.
- A. a multicore, multiprocessor system.
- B. relevant training data.
- C. a threat feed API.
- D. anomalous traffic signatures.
Answer: D
NEW QUESTION 163
While analyzing logs from a WAF, a cybersecurity analyst finds the following:
Which of the following BEST describes what the analyst has found?
- A. This is an encoded WAF bypass
- B. This is an encrypted packet
- C. This is an encrypted GET HTTP request
- D. A packet is being used to bypass the WAF
Answer: A
NEW QUESTION 164
The new Chief Technology Officer (CTO) is seeking recommendations for network monitoring services for the local intranet. The CTO would like the capability to monitor all traffic to and from the gateway, as well as the capability to block certain content. Which of the following recommendations would meet the needs of the organization?
- A. Recommend installation of a firewall on the internal interface and a NIDS on the external interface of the gateway router.
- B. Recommend installation of an IPS on both the internal and external interfaces of the gateway router.
- C. Recommend setup of IP filtering on both the internal and external interfaces of the gateway router.
- D. Recommend installation of an IDS on the internal interface and a firewall on the external interface of the gateway router.
Answer: A
NEW QUESTION 165
Which of the following technologies can be used to house the entropy keys for task encryption on desktops and laptops?
- A. Bus encryption
- B. TPM
- C. HSM
- D. Self-encrypting drive
Answer: D
NEW QUESTION 166
The Chief Information Officer (CIO) for a large manufacturing organization has noticed a significant number of unknown devices with possible malware infections are on the organization's corporate network.
Which of the following would work BEST to prevent the issue?
- A. Reconfigure the NAC solution to prevent access based on a full device profile and ensure antivirus is installed.
- B. Update the antivirus configuration to enable behavioral and real-time analysis on all systems within the network.
- C. Segment the network to isolate all systems that contain highly sensitive information, such as intellectual property.
- D. Implement certificate validation on the VPN to ensure only employees with the certificate can access the company network.
Answer: A
NEW QUESTION 167
Review the following results: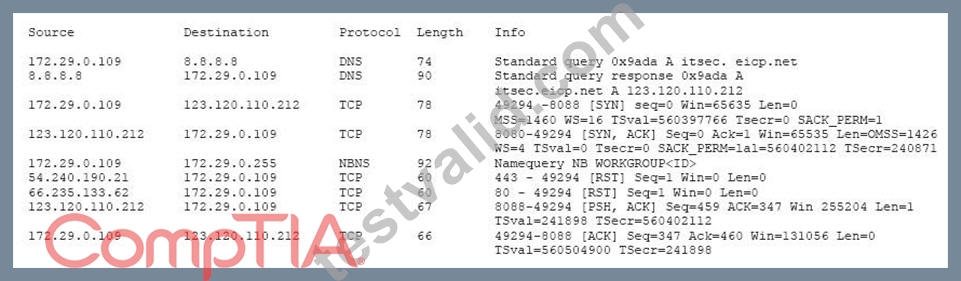
Which of the following has occurred?
- A. This is normal network traffic.
- B. 172.29.0.109 is infected with a worm.
- C. 123.120.110.212 is infected with a Trojan.
- D. 172.29.0.109 is infected with a Trojan.
Answer: A
NEW QUESTION 168
A security analyst performed a review of an organization's software development life cycle. The analyst reports that the life cycle does not contain in a phase in which team members evaluate and provide critical feedback on another developer's code. Which of the following assessment techniques is BEST for describing the analyst's report?
- A. Architectural evaluation
- B. Whitebox testing
- C. Peer review
- D. Waterfall
Answer: C
NEW QUESTION 169
A Linux-based file encryption malware was recently discovered in the wild. Prior to running the malware on a preconfigured sandbox to analyze its behavior, a security professional executes the following command:
umount *a *t cifs,nfs
Which of the following is the main reason for executing the above command?
- A. To limit the malware's reach to the local host.
- B. To test if the malware affects remote systems
- C. To ensure the malware is memory bound.
- D. To back up critical files across the network
Answer: A
NEW QUESTION 170
......
CS0-002 Exam Dumps, CS0-002 Practice Test Questions: https://lead2pass.testvalid.com/CS0-002-valid-exam-test.html