


Our experts have made their best efforts to provide you current exam information about EC-Council Certified Security Analyst (ECSA) practice test for your exam preparation. The contents of our training materials applied to every stage of candidates who have no or rich experience in the EC-COUNCIL lead4pass review. A little attention to these study materials will improve your ability to get through EC-Council Certified Security Analyst (ECSA) test questions with high pass rate. Our EC-Council Certified Security Analyst (ECSA) valid vce is the best alternative to your time and money to get an excellent career in the IT filed. Our valid EC-Council Certified Security Analyst (ECSA) test answers contain everything you want to overcome the difficulties of the real exam, that's the reason that we keep the popularity among the vendors of ECSAv8 lead4pass dumps.

Our ECSA pass guide is designed to solve all the difficulties of the candidates in the best possible way. For this reason we offer pdf format and online test engine version for complete preparation of EC-Council Certified Security Analyst (ECSA) practice test. With the help of our learning materials, especially the online practice exam, you can practice EC-Council Certified Security Analyst (ECSA) test questions in the formal test environment and test your skills regarding EC-Council Certified Security Analyst (ECSA) pass guaranteed. In this way we assure you with 100% result and full refund guarantee on our EC-Council Certified Security Analyst (ECSA) lead4pass review. Besides, our online version will also remark your mistakes made in the EC-Council Certified Security Analyst (ECSA) practice test and thus you can learn from your mistakes and avoid them in the real exam.
Our website offers you the best solutions for ECSAv8 pass guaranteed in an easy and smart way. The latest EC-Council Certified Security Analyst (ECSA) test questions are written by our certified trainers who have studied IT certification exam study guide for long time. You can totally rest assured the accuracy of our EC-Council Certified Security Analyst (ECSA) test answers because we keep check the updating of EC-Council Certified Security Analyst (ECSA) lead4pass review every day. If you still doubt our products, you can download the free demo to have a try.
Comparing to attending training classes, choose our EC-Council Certified Security Analyst (ECSA) valid vce as your exam preparation materials will not only save your time and money, but also save you from the failure of EC-Council Certified Security Analyst (ECSA) practice test. One or two days' preparation will be enough to the test and you just need to remember the EC-Council Certified Security Analyst (ECSA) test answers in-depth, you will get good result finally. Please feel free to contact us if you have any questions.
Instant Download ECSAv8 Exam Braindumps: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
EC-COUNCIL ECSAv8 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Topic 1: Network Attacks and Defense Evasion | - IDS/Firewall evasion techniques - Sniffing and session hijacking |
| Topic 2: Information Security Assessment Methodologies | - Risk analysis and vulnerability assessment approaches - Security assessment planning and scoping |
| Topic 3: Penetration Testing Life Cycle | - Exploitation and post-exploitation techniques - Information gathering and reconnaissance - Pre-engagement interactions and rules of engagement - Reporting and remediation recommendations |
| Topic 4: Web Application Penetration Testing | - SQL injection and XSS attacks - OWASP Top 10 vulnerabilities |
| Topic 5: System Hacking and Privilege Escalation | - Privilege escalation methods - Password attacks and cracking techniques |
| Topic 6: Wireless and Mobile Attacks | - Wireless network vulnerabilities - Mobile application security testing basics |
| Topic 7: Social Engineering | - Phishing and impersonation techniques - Human-based attack vectors |
| Topic 8: Reporting and Documentation | - Security assessment reporting structure - Risk communication and remediation guidance |
| Topic 9: Network Scanning and Enumeration | - Service and OS fingerprinting - Port scanning techniques and tools |
EC-COUNCIL EC-Council Certified Security Analyst (ECSA) Sample Questions:
Which of the following methods is used to perform server discovery?
- A. Whois Lookup
- B. SQL Injection
- C. Session Hijacking
- D. Banner Grabbing
Correct Answer: A 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
John, a penetration tester, was asked for a document that defines the project, specifies goals, objectives, deadlines, the resources required, and the approach of the project. Which of the following includes all of these requirements?
- A. Penetration testing project plan
- B. Penetration testing project scope report
- C. Penetration testing schedule plan
- D. Penetration testing software project management plan
Correct Answer: A 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
Which of the following are the default ports used by NetBIOS service?
- A. 134, 135, 136, 137
- B. 137, 138, 139, 140
- C. 135, 136, 139, 445
- D. 133, 134, 139, 142
Correct Answer: B 🗳️
The amount of data stored in organizational databases has increased rapidly in recent years due to the rapid advancement of information technologies. A high percentage of these data is sensitive, private and critical to the organizations, their clients and partners.
Therefore, databases are usually installed behind internal firewalls, protected with intrusion detection mechanisms and accessed only by applications. To access a database, users have to connect to one of these applications and submit queries through them to the database. The threat to databases arises when these applications do not behave properly and construct these queries without sanitizing user inputs first.
Identify the injection attack represented in the diagram below: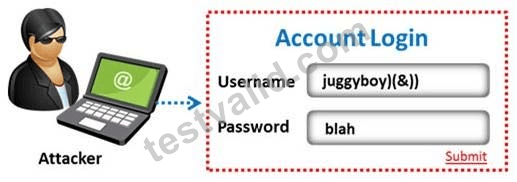
- A. Frame Injection Attack
- B. XPath Injection Attack
- C. SOAP Injection Attack
- D. LDAP Injection Attack
Correct Answer: D 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
What is the difference between penetration testing and vulnerability testing?
- A. Vulnerability testing is more expensive than penetration testing
- B. Penetration testing is conducted purely for meeting compliance standards while vulnerability testing is focused on online scans
- C. Penetration testing is based on purely online vulnerability analysis while vulnerability testing engages ethical hackers to find vulnerabilities
- D. Penetration testing goes one step further than vulnerability testing; while vulnerability tests check for known vulnerabilities, penetration testing adopts the concept of 'in-depth ethical hacking'
Correct Answer: D 🗳️

 Kerr

 Janice
 Ed
 Les

 Martina

 Ives
 Moore
 Warner
 Alston
 Gavin
 Gene
 Christine
 Georgia
 Maxwell
 Harold
 Ted
 Antoine
 Tiffany
 Grace


