


Microsoft SC-200 certified professional salary
The average salary of Microsoft Security Operations Analyst Professional
India: 6841215 INR
United States: 90,000 USD
UK: 67942 Pounds
Our experts have made their best efforts to provide you current exam information about Microsoft Security Operations Analyst practice test for your exam preparation. The contents of our training materials applied to every stage of candidates who have no or rich experience in the Microsoft lead4pass review. A little attention to these study materials will improve your ability to get through Microsoft Security Operations Analyst test questions with high pass rate. Our Microsoft Security Operations Analyst valid vce is the best alternative to your time and money to get an excellent career in the IT filed. Our valid Microsoft Security Operations Analyst test answers contain everything you want to overcome the difficulties of the real exam, that's the reason that we keep the popularity among the vendors of SC-200 lead4pass dumps.

Our Microsoft Certified: Security Operations Analyst Associate pass guide is designed to solve all the difficulties of the candidates in the best possible way. For this reason we offer pdf format and online test engine version for complete preparation of Microsoft Security Operations Analyst practice test. With the help of our learning materials, especially the online practice exam, you can practice Microsoft Security Operations Analyst test questions in the formal test environment and test your skills regarding Microsoft Security Operations Analyst pass guaranteed. In this way we assure you with 100% result and full refund guarantee on our Microsoft Security Operations Analyst lead4pass review. Besides, our online version will also remark your mistakes made in the Microsoft Security Operations Analyst practice test and thus you can learn from your mistakes and avoid them in the real exam.
Our website offers you the best solutions for SC-200 pass guaranteed in an easy and smart way. The latest Microsoft Security Operations Analyst test questions are written by our certified trainers who have studied IT certification exam study guide for long time. You can totally rest assured the accuracy of our Microsoft Security Operations Analyst test answers because we keep check the updating of Microsoft Security Operations Analyst lead4pass review every day. If you still doubt our products, you can download the free demo to have a try.
Comparing to attending training classes, choose our Microsoft Security Operations Analyst valid vce as your exam preparation materials will not only save your time and money, but also save you from the failure of Microsoft Security Operations Analyst practice test. One or two days' preparation will be enough to the test and you just need to remember the Microsoft Security Operations Analyst test answers in-depth, you will get good result finally. Please feel free to contact us if you have any questions.
Instant Download SC-200 Exam Braindumps: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
How to Register For Exam SC-200: Microsoft Security Operations Analyst?
Exam SC-200: Microsoft Security Operations Analyst
The Microsoft Security Operations Analyst collaborates with organizational stakeholders to secure information technology systems for the organization. Their goal is to reduce organizational risk by rapidly remediating active attacks in the environment, advising on improvements to threat protection practices, and referring violations of organizational policies to appropriate stakeholders.
Responsibilities include threat management, monitoring, and response by using a variety of security solutions across their environment. The role primarily investigates, responds to, and hunts for threats using Microsoft Azure Sentinel, Azure Defender, Microsoft 365 Defender, and third-party security products. Since the Security Operations Analyst consumes the operational output of these tools, they are also a critical stakeholder in the configuration and deployment of these technologies.
Part of the requirements for: Microsoft Certified: Security Operations Analyst Associate
Reference: https://docs.microsoft.com/en-us/learn/certifications/exams/sc-200
Microsoft SC-200 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Mitigate threats using Microsoft Defender for Cloud Apps | 20-25% | - Configure Microsoft Defender for Cloud Apps
|
| Topic 2: Mitigate threats using Microsoft Defender for Identity | 15-20% | - Configure Microsoft Defender for Identity
|
| Topic 3: Mitigate threats using Microsoft 365 Defender | 25-30% | - Hunt threats in Microsoft 365 Defender
|
| Topic 4: Mitigate threats using Microsoft Defender for Endpoint | 25-30% | - Manage devices and monitor threats
|
Microsoft Security Operations Analyst Sample Questions:
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint and contains a user named user1 and a Microsoft 365 group named Group1. All users are assigned a Defender for Endpoint Plan 1 license.
You enable Microsoft Defender XDR Unified role-based access control (RBAC) for Endpoints & Vulnerability Management.
You need to ensure that User1 can configure alerts that will send email notifications to Group1. The solution must follow the principle of least privilege.
Which permissions should you assign to User1?
- A. Defender Vulnerability Management - Remediation handling
- B. Manage security settings
- C. Live response capabilities: Basic
- D. Alerts investigation
Correct Answer: B 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
You have a Microsoft 365 subscription.
You have 1,000 Windows devices that have a third-party antivirus product installed and Microsoft Defender Antivirus in passive mode.
You need to ensure that the devices are protected from malicious artifacts that were undetected by the third - party antivirus product.
Solution: You configure endpoint detection and response (EDR) in block mode.
Does this meet the goal?
- A. Yes
- B. No
Correct Answer: A 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
You have an Azure subscription that has the enhanced security features in Microsoft Defender for Cloud enabled and contains a user named User1.
You need to ensure that User1 can export alert data from Defender for Cloud. The solution must use the principle of least privilege.
Which role should you assign to User1?
- A. Reader
- B. Contributor
- C. Owner
- D. User Access Administrator
Correct Answer: A 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
You have an Azure subscription named Sub1 that uses Microsoft Defender for Cloud.
You need to assign the PCI DSS 4.0 initiative to Sub1 and have the initiative displayed in the Defender for Cloud Regulatory compliance dashboard.
From Security policies in the Environment settings, you discover that the option to add more industry and regulatory standards is unavailable.
What should you do first?
- A. Enable the Cloud Security Posture Management (CSPM) plan for the subscription.
- B. Disable the Microsoft Cloud Security Benchmark (MCSB) assignment.
- C. Configure the Continuous export settings for Azure Event Hubs.
- D. Configure the Continuous export settings for Log Analytics.
Correct Answer: A 🗳️
Explanation: Only visible for TestValid members. You can sign-up / login (it's free).
You manage the security posture of an Azure subscription that contains two virtual machines name vm1 and vm2.
The secure score in Azure Security Center is shown in the Security Center exhibit. (Click the Security Center tab.)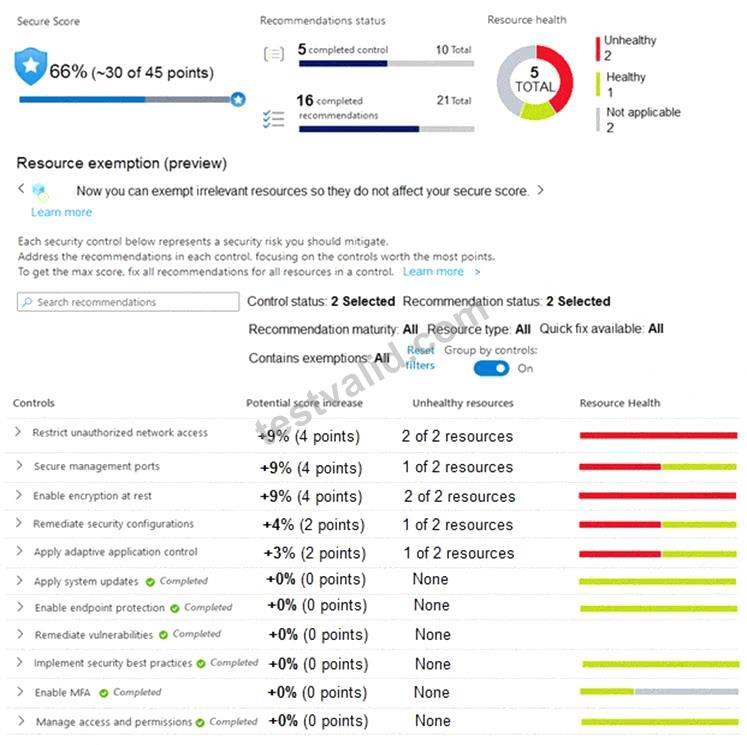
Azure Policy assignments are configured as shown in the Policies exhibit. (Click the Policies tab.)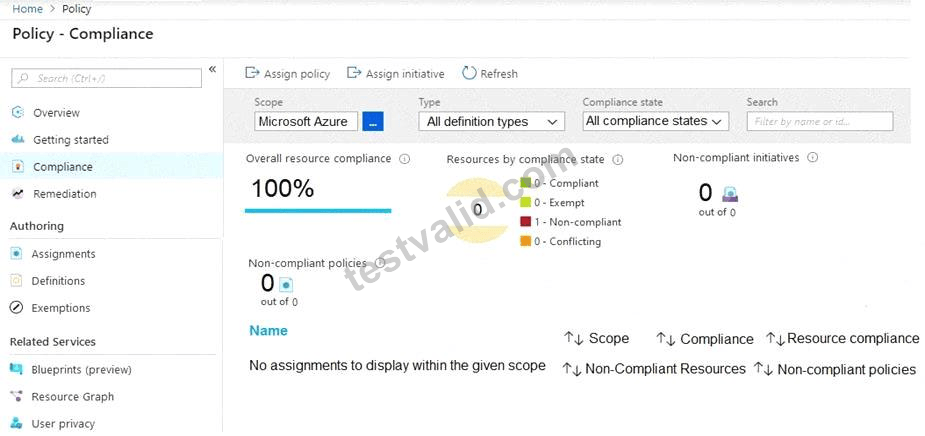
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.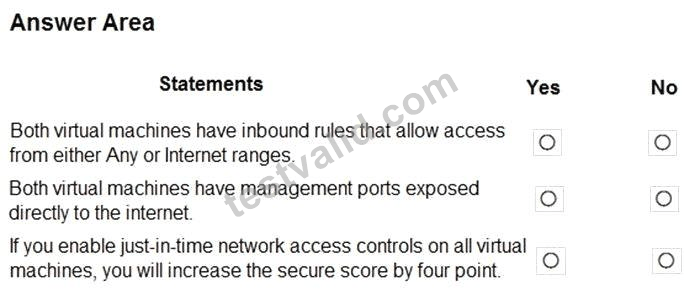
Correct Answer:

Explanation:
Statements
Answer
Both virtual machines have inbound rules that allow access from either Any or Internet ranges.
Yes
Both virtual machines have management ports exposed directly to the internet.
Yes
If you enable just-in-time network access controls on all virtual machines, you will increase the secure score by four points.
Yes
In the Microsoft Defender for Cloud (Azure Security Center) screenshot, the Secure Score report shows several active security recommendations, including:
"Restrict unauthorized network access" with a potential score increase of +9% (4 points) for 2 of 2 resources.
"Secure management ports" with a potential score increase of +9% (4 points) for 1 of 2 resources.
These controls correspond to Defender for Cloud recommendations related to network security and exposure of management ports (RDP/SSH). The fact that both controls show "2 of 2 resources" or "1 of 2 resources" as unhealthy means both virtual machines currently have NSG or firewall rules that allow inbound access from
"Any" or "Internet ranges," indicating open ports and insecure configurations.
According to Microsoft documentation ("Improve your Secure Score in Microsoft Defender for Cloud"), enabling Just-In-Time (JIT) VM access mitigates these findings by restricting inbound RDP/SSH access to approved users for limited time windows, thereby increasing the Secure Score. Each remediated recommendation increases the Secure Score by the number of points shown in the "Potential score increase" column (4 points in this case).
Because Azure Policy shows no assigned or conflicting policies, compliance enforcement is not yet active, confirming that the current exposure is due to lack of configuration rather than policy override.
Therefore:
The two VMs have inbound Internet-accessible rules # Yes.
They have management ports exposed # Yes.
Enabling JIT network access would fix both recommendations, improving the Secure Score by 4 points # Yes.
Viewing page 1 out of 87 pages.
Viewing questions 1-5 out of 435 questions.

 Celeste

 Conrad

 Len
 Benjamin
 Duke
 Armstrong
 Tiffany

 Hale
 Yetta
 Norman
 Joshua
 Newman
 Dana
 Elroy
 Jeffrey
 Lyndon
 Gill
 Rosalind
 Morton
 Raymond
 Emmanuel
 Bruno
 Natividad


